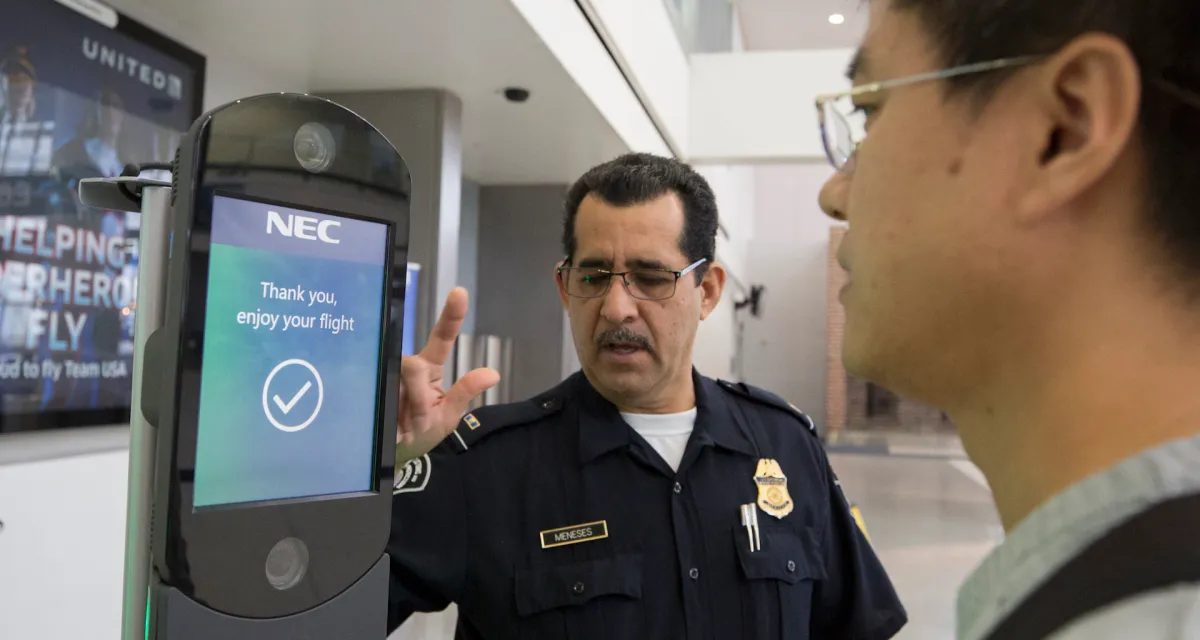
The European Parliament will soon be asked to consent to an agreement that sets rules for US border authorities to query European national systems, including fingerprint records. The Commission sent it to the Council on 10 September and says a 31 December visa waiver deadline makes provisional application urgent. Before voting, Parliament should read a memo about how the US Department of Homeland Security (DHS) handled its own data in 2023.
Table of contents
The memo is old, and it did not involve European data. Its value is what it shows about who checks the checkers at DHS.
What the memo says
HSIN-Intel, the intelligence section of the Homeland Security Information Network, was meant to be limited to its own users. A misconfiguration set access to everyone, so restricted material was visible to all users of a network with tens of thousands of accounts (reported in September 2025).
The material was sensitive but unclassified: law enforcement tips, reports on foreign hacking and disinformation, and analysis of domestic protest movements.
According to Security Magazine, the memo counts 439 intelligence products accessed improperly 1,525 times between March and May 2023. Of those accesses, 518 came from the private sector and 46 from non-US citizens, mostly for cybersecurity material. The memo reached the public through a Freedom of Information Act request by the Brennan Center for Justice.
Read also: Europe’s Surveillance Rules Are Being Written Around the Exceptions
How the safeguards performed
The DHS Office of Privacy first rated the impact “minimal to low”. The memo’s author found that the office had not fully considered the personal information exposed, particularly that of Americans, and recommended retraining intelligence staff on what counts as such information. Security Magazine adds that the memo did not assess the impact on other agencies that share information through the hub.
A DHS spokesperson said the intelligence office fixed the problem immediately and investigated potential harm, and that several oversight bodies afterwards found no impactful or serious security breach. That is a fair summary of the department’s position, and it should be read next to the memo’s own finding that the first assessment missed part of the picture.
What the agreement contains
Negotiations with Washington ended on 23 July and that the framework has not been signed. It sets common rules for how US authorities and participating EU states may query each other’s national systems for border checks and visa or travel authorisation decisions.
It does not open European databases to DHS and is not by itself a legal basis for transferring personal data, because actual exchanges depend on bilateral agreements.
Automated queries need a risk-based justification, query volumes will be capped in the bilateral deals, reciprocity applies, and facial images are not allowed as a search input. These are real limits, and they are the strongest argument for approving the framework.
What changed from the Commission’s own starting point
The text differs from the Commission’s negotiating recommendation from July 2025. Automated decisions with significant adverse effects are now allowed where domestic law authorises them with safeguards, where the original proposal would have barred them. The agreement does not specify when a human must intervene.
There is no uniform retention limit, because each side sets periods under its own law, and the narrower limit on retention after departure was dropped. Onward transfers to third countries or international organisations are permitted with the originating authority’s prior consent, where the recommendation would have prohibited them.
Who oversees it
The European Data Protection Supervisor warned during the talks that the framework could become the first EU agreement involving large-scale sharing of personal and biometric data with a third country for border and immigration control, and urged a narrow scope and US judicial redress regardless of citizenship.
Read also: Europe’s Digital ID Will Outlive Its Promises
The agreement provides access and correction rights and requires administrative and judicial remedies. EU oversight falls to national data protection authorities, while US oversight may be split among several privacy, accountability and inspector-general bodies. A joint committee meets at least annually, and the first joint review must come within three years of entry into force.
That structure is the one the DHS memo tested. In 2023 the check on a data exposure was internal, and the first verdict was a rating of “minimal to low”. The public learned the detail two years later because a civil rights group filed a records request. A framework whose oversight is each side’s own, reviewed after three years, asks Europe to rely on the same kind of assurance.
What Parliament should ask for
I would use the consent vote to ask for four things. Restore the bar on automated decisions with significant adverse effects, or require a human decision before any such effect. Restore the ban on onward transfers.
Set a uniform retention limit. Give an independent body audit rights over how EU-originated queries are handled, with a fixed deadline for notifying EU authorities of any exposure.
The other side of the argument
The memo describes one misconfiguration that was fixed, and DHS says oversight bodies found no serious breach. The 46 non-US accesses are not identified as European. The deadline is real: the Commission argues that missing it puts visa-free travel at risk, and security cooperation with the US has benefits. I have not seen where the Council stands after 10 September, so my argument rests on the text as it has been reported.
SOURCES & METHOD
How this article was made. This is an opinion piece resting on four sources. The DHS memo and the agreement text were not read directly, and WIRED was read through a mirror copy. The exposure is from 2023 and was reported in 2025. The Council’s position after 10 September and the date of the Parliament vote were not checked.
Sources
- Biometric Update: EU sends US biometric border-sharing deal to Council as deadline looms (September 2026) – the content, the changes from 2025, the deadline and the oversight structure.
- European Parliamentary Research Service: Negotiating the Enhanced Border Security Partnership (28 September 2026) – the approval procedure and the scope of the data.
- Security Magazine: Sensitive intel exposed, DHS data hub accessible to thousands (22 September 2025) – the dates, the 439 products, 1,525 accesses and the Brennan Center memo.
- WIRED, mirror copy: A DHS data hub exposed sensitive intel to thousands of unauthorized users – the misconfiguration, the privacy assessment and the DHS response.