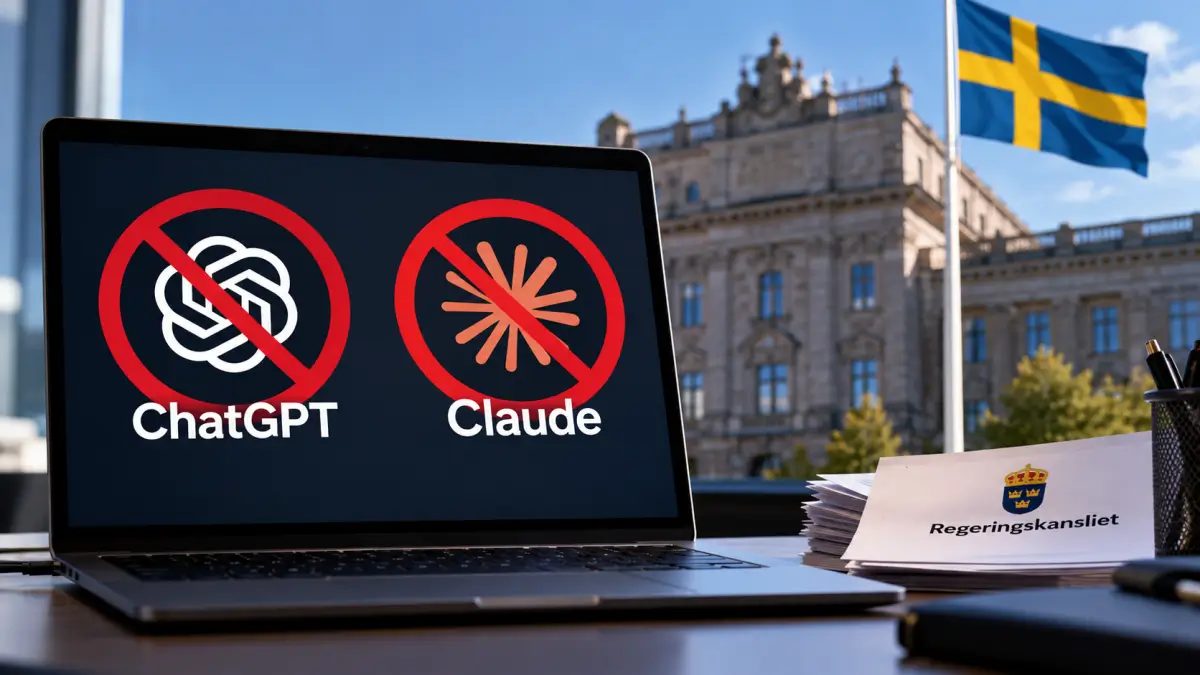
A civil servant at Sweden’s Government Offices can no longer open ChatGPT or Claude on a work computer. The European Commission has told its staff never to share anything non-public with online chatbots. In four Austrian federal ministries, an audit found mostly no rules at all. One question, what a public employee may put into a chatbot, gets three different answers inside Europe, and the Swedish chatbot ban is the sharpest of them.
Table of contents
How Sweden’s chatbot ban works
From Monday 26 October, ChatGPT and Claude are blocked on staff computers at the Government Offices, the body that supports the prime minister and cabinet. Microsoft Copilot is among the approved tools, and its security was tightened after a review, though the press service declined to give details. Some employees keep access to both blocked tools through an AI platform the Government Offices built itself.
The stated reason is data. Mikael Wettercrantz, the director of digitalisation, declined an interview with Ekot, Sveriges Radio’s news programme, but wrote on the staff intranet that using AI services without an agreement can have “consequences for our information security”.
Ekot’s survey found that the Government Offices are not alone. The Tax Agency and the National Board of Institutional Care (Sis) have imposed locks, and the Enforcement Authority is preparing its position. The Government Offices had earlier restricted the Chinese service DeepSeek.
The sharpest description of the risk comes from the Transport Administration. Its internal audit earlier this year found widespread and risky use of about ten AI services, and recorded “several examples of problematic use of open AI services”, concerning both the sensitivity of the information entered and how the AI-generated answers were handled.
The Commission’s rule already says no
The European Commission’s internal guidelines for staff on online generative AI tools rest on one flat rule: “Staff must never share any information that is not already in the public domain.” The rule covers personal data, sensitive non-classified information and classified information.
The reasoning is mechanical. Anything typed into a chatbot goes to the provider, which may use it to generate future outputs that could reach the public. The guidelines also bar pasting AI output straight into official texts and using these tools for critical or time-sensitive processes, and they remind staff of their confidentiality duties under the Staff Regulations.
That is a written rule for staff. A rule of that kind depends on the person remembering it at the moment of pasting, and personal data is covered, so a name typed into a prompt counts.
Read also: European Governments Went Dark Over a PHP Flaw Whose Fix Stalled
Parliament switched off the assistants
In February the European Parliament disabled built-in AI features on work devices used by members and their staff, according to an internal email. The features included writing assistants, summarisers for text and web pages, and enhanced virtual assistants. Email, calendar and standard apps kept working.
Parliament’s IT support said some features use cloud services for tasks that could run locally, which sends data off the device, and that the scale of data shared with providers was still unclear. Until that was settled, the team wrote, “it is considered safer to keep such features disabled”.
Members were also asked not to expose official emails, documents or internal information to AI tools that scan or analyse content, and to be careful with third-party AI apps and with personal phones or tablets used for work.
The record differs on scope. Decrypt’s summary says Parliament disabled ChatGPT, Claude and Copilot, while eWeek’s account of the email says it did not specify which AI systems were switched off. Both agree on the motive: data leaving the device for providers whose handling of it was unclear, the problem IT support itself described.
Capitals disagree on the default
France’s Prime Minister’s services issued a charter on generative AI in June 2025 that follows much of Sweden’s logic without a block. It treats public AI tools as outside parties: only public, freely usable data (open data) may go to an external AI, and working drafts of documents meant for publication do not count as public.
Personal and sensitive data, and information of restricted, classified or confidential level, may not be entered, and staff in doubt must seek their superiors’ approval.
The charter also bars handing production or decisions over to the tool and calls fully automated decisions without human intervention inappropriate. It presents its rules as a stopgap until sovereign AI for state services is rolled out, which it says will remove some of the risks it lists.
Germany sits between the two poles. The federal guidelines for AI in the administration, issued by the Interior Ministry and dated March 2025, leave it to each agency head to decide whether and which AI systems may be used, and allow registration with an external AI service only after the IT officials approve it, with opinions from the data protection, secrecy and information security officers.
Private accounts and devices are not allowed, and use of the data for training should be prevented where possible.
Classified information may be entered only into a system explicitly approved for it, and for externally run systems the guidelines describe the most restrictive case as clearance for public data only. Special categories of personal data, such as health data, are in principle barred, with exceptions under the GDPR. Berlin neither blocks nor waves through: it leaves the decision to each agency.
Austria shows the other end. In a report on four federal ministries and the federal computing centre BRZ, covering mainly 2021 to 2023, the Court of Audit found mostly no rules for how staff may use publicly available AI tools such as ChatGPT or DeepL. Only the former climate ministry asked staff to flag such use.
By June 2024 the four ministries had 35 AI applications and projects in use, with no overall overview across the state. The auditors also recommend building staff AI skills through recruitment and training, and only the finance ministry had specially trained staff for AI tasks.
What the data protection supervisor expects
The European Data Protection Supervisor (EDPS), which oversees the EU institutions, has set out what they must do when generative AI touches personal data. The data protection rules for EU institutions apply in full. Each use needs a valid legal basis, and consent is hard to rely on given how these systems are trained. The institution must also define who is controller and who is processor, which is what a contract with a vendor settles.
A data protection impact assessment is required before high-risk processing, and personal data must be limited to what is necessary. Training data and outputs have to be verified, since the systems can produce false information, and security controls must cover threats such as prompt injection and model inversion.
Wettercrantz’s argument about services without an agreement fits this frame. Free consumer chatbots come without such a contract, which leaves the employer to permit them under written rules or to block them.
Read also: Europe Writes AI Rules for Systems It Rents
Sweden’s line is blurrier than the headlines
The block has holes. Some staff still reach both tools through the in-house platform. Microsoft reportedly added Claude models to Copilot in early 2026, administrators in the EU must switch them on, and the Government Offices has not confirmed whether Claude is enabled in its Copilot. A tool on the banned list and one on the approved list may therefore overlap.
The analysis reads this as a transfer of responsibility. A written rule leaves the risk with the employee, who must remember it at the moment of pasting. A block moves it to the network and to the contract the employer signs.
No source opened for this analysis shows a single EU-wide rule on public employees and chatbots. Stockholm blocks, Berlin leaves it to each agency, Paris allows only public data for outside tools, and the four Austrian ministries the auditors examined mostly had no rule to break.
BASIS OF ANALYSIS
Basis of analysis. The analysis rests on eight sources: Sveriges Radio’s report and Decrypt’s on the Swedish decision, the Commission’s staff guidelines, the EDPS guidance, the German federal guidelines, the French prime minister’s services’ charter, the Austrian audit court’s press release and a report on Parliament’s email. The Swedish intranet post and the Parliament email were not available and are reproduced through media. No EU-wide rule on public employees’ use of chatbots could be confirmed.
Sources
- Sveriges Radio: Chat GPT och Claude förbjuder Regeringskansliet (23 October 2026) – the block, Wettercrantz’ intranet comment, other agencies and the Transport Administration audit.
- Decrypt: Sweden’s Government Offices Block ChatGPT and Claude, Keep Microsoft Copilot (24 October 2026) – the reasoning, Wettercrantz’s statements and the caveat on Claude inside Copilot and the account of Parliament’s decision.
- European Commission: Guidelines on the use of online generative AI tools (undated, freedom-of-information release) – the staff rules and their reasons.
- European Data Protection Supervisor: First EDPS orientations for EUIs using generative AI – legal basis, roles, impact assessments and safeguards.
- eWeek: European Parliament Blocks AI on Lawmakers’ Devices Over Security Fears (18 February 2026) – Parliament’s decision and the IT support email.
- Rechnungshof Österreich: Press release on AI in the federal administration (20 June 2025) – missing staff rules and the number of AI applications.
- German Interior Ministry: Leitlinien für den Einsatz Künstlicher Intelligenz in der Bundesverwaltung (March 2025) – who decides, registration, accounts and data rules for external AI services.
- Services du Premier ministre: Charte relative à l’utilisation de l’IA générative (June 2025) – public-data-only rule for external AI and prohibited uses.