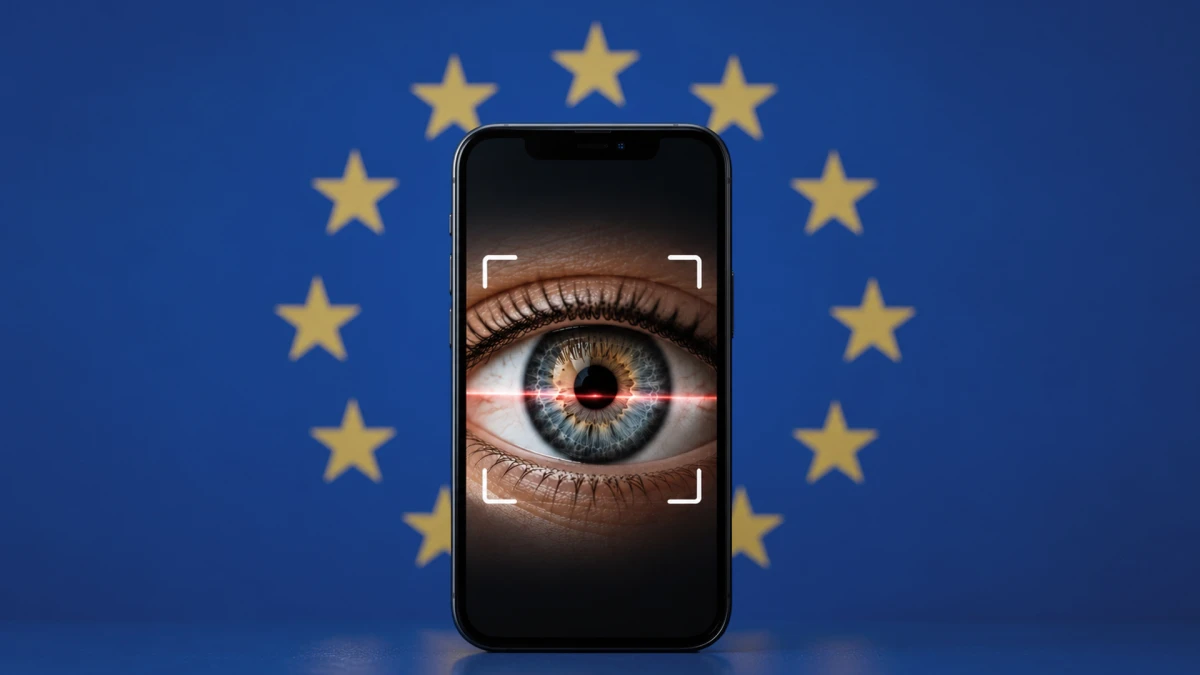
Every message you send from your phone passes through a company’s servers or, if it is end-to-end encrypted, through nobody’s. For four years Europe has argued over whether a law should change that in the name of protecting children. The proposal has a formal title, the Child Sexual Abuse Regulation. Almost everyone else calls it Chat Control.
Table of contents
The fight is not simple, and neither side is inventing the thing it cares about. Child protection groups and police say they lose leads when platforms stop looking for abuse material. Cryptographers and privacy lawyers say a duty to scan cannot be built without weakening everyone’s security. This guide sets out both cases and then follows the file from the Commission’s proposal in 2022 to the stalled talks of this autumn.
A note on what is settled and what is not. The Council negotiates mostly behind closed doors, so several dates below come from advocacy trackers and press reports rather than official records. Where a claim rests on one side’s account, the text says so, and the points I could not confirm in a primary document are listed at the end.
Two laws with one nickname
The nickname covers two separate laws. Chat Control 1.0 is a temporary exception from the EU’s ePrivacy rules, Regulation (EU) 2021/1232, that allows companies to scan private messages voluntarily for child abuse material. Chat Control 2.0 is the permanent regulation that the Commission proposed on 11 May 2022. Mixing them up is the most common mistake in the debate, and both camps make it when it suits them.
The 2021 exception does not oblige anyone to scan. It gives legal cover to platforms that choose to do so. The Electronic Frontier Foundation notes that voluntary scanning is not technically legal in the EU without that exception, which is why the exception exists and why its expiry mattered so much to the companies and the police who rely on their reports.
The permanent law would build a lasting system. Providers would have to assess how their services can be abused and take measures to reduce the risk. A new EU Centre would coordinate detection technology and pass confirmed cases on to Europol and national police. The original proposal also let authorities order providers to detect abuse material, including on encrypted services, and the question of whether such orders survive has driven every round of talks since.
The two laws are tied together. What happens to the temporary exception shapes the bargaining over the permanent regulation, as the next sections show. The Center for Democracy and Technology warned this summer that reviving the exception could undermine progress on the permanent law, while supporters argue that the exception buys time for a proper deal.
The case for scanning
Read also: Chat Control Is Mass Surveillance in Disguise
The strongest argument for the law is about leads. Platforms based in the United States have to report suspected child abuse material to the National Center for Missing and Exploited Children, which forwards reports to police around the world. According to figures the Commission itself cited, the Center received more than 21 million reports in 2020, of which over one million concerned EU member states.
The Internet Watch Foundation, a British charity that runs a hash list of known abuse images, argues that law enforcement depends on that flow. It points to late 2020, when companies were unsure whether scanning was legal under EU law, and says reports from EU accounts to the Center fell by 58 percent in 18 weeks.
That is one organisation’s account of its own field, and critics dispute what the drop proves, but nobody disputes that the reports are a main source of leads.
Europol makes a related point. Its executive director, Catherine De Bolle, warned before the temporary rules lapsed that removing the legal basis would cause a serious reduction in referrals and severely impair investigative leads. Euronews reports Europol’s view that abuse material is increasingly shared on large mainstream platforms, where offenders use encryption and anonymity.
The effects show up in national statistics. A Swedish police official told the news agency TT that the police received 25,077 reports from the Center in the previous year, and that the force would evaluate after a while whether numbers rose or fell once the temporary rules lapsed. Children’s rights groups such as ECPAT say the police agree that the legislation is needed.
Supporters also reject the label. The Commissioner for internal affairs and migration, Magnus Brunner, has refused the term Chat Control. TechRadar reports that he told MEPs he preferred Parliament’s position to the Council’s text, while still regarding the Commission’s original 2022 proposal as the best option.
The supporters’ position is that platforms already scan public content, and that the aim is to find a small amount of illegal material, not to read conversations.
Any honest account has to grant two things. The material is real, the harm to children is severe, and the volume of reports is large. The people arguing for the law include child protection charities that have worked on this for decades. Reducing the case for scanning to a pretext for surveillance, as some critics do, misses what many of its supporters actually want.
The case against, from lawyers and cryptographers
The critics’ strongest argument is technical. Scanning a message before it is encrypted, known as client-side scanning, puts detection software on every device.
Nearly 500 researchers from 34 countries signed an open letter in September 2025 calling the latest draft technically infeasible and warning that on-device scanning creates a single point of failure.
The scientists’ second point is accuracy. They argue that scanning billions of messages and images a day cannot reach the accuracy required, that even a low false-positive rate would flood the authorities with reports of innocent users, and that small edits to an image can defeat state-of-the-art detectors. They also challenge the plan to use machine learning to find previously unseen material.
The legal case runs in parallel. In 2023, advice dated 26 April from the Council’s own legal service leaked, saying there was a high probability that detection orders aimed at all users of a service would amount to general and indiscriminate surveillance.
A former judge of the EU’s Court of Justice, Christopher Vajda, wrote a separate opinion for the Pirate Party MEP Patrick Breyer concluding that the plans would fail in court. Mr Breyer commissioned it, which readers should weigh. The European data protection authorities warned against generalised, indiscriminate scanning in a joint opinion in 2022.
Some companies have said they would act. The German encrypted email provider Tuta said that implementing client-side scanning would violate its commitment to end-to-end encryption, and that it would either sue the EU or stop operating in Europe. Whether other providers would do the same is unknown, and no provider has been ordered to scan under the permanent law because it does not exist yet.
The critics also point at function creep. Once a system exists that can look for one kind of illegal material in private messages, the argument goes, it can be widened to others, and a less democratic government could use the same infrastructure. Supporters answer that the proposal contains safeguards. Our own analysis of Europe’s surveillance rules traces how such exceptions have tended to grow in other laws.
How the Council gave way
For most of 2025 the Council could not agree on its position. The file stalled against opposition from governments including Germany. According to a tracker run by Reclaim The Net, Germany opposed mandatory scanning on 8 October 2025, and the Danish presidency then dropped detection orders from its text. That tracker is an advocacy site, and the dates should be checked against the Council’s own records.
On 26 November 2025 the governments’ representatives in the Council agreed a negotiating mandate. It removed the explicit duty to scan all private messages.
Instead it relied on risk assessments, mitigation measures for platforms and voluntary detection, and it extended the legal basis for voluntary scanning indefinitely, according to press reports. The Parliament’s position from 2023, which rules out scanning encrypted services and requires court authorisation, stood on the other side.
Privacy groups did not accept that this was a retreat. Mullvad, the VPN provider, argued that the Council’s version opens the door to surveillance infrastructure, citing vaguely worded rules that could require age verification and identity checks, including on encrypted services.
Others called the text a political deception. Those are critics’ readings, and the Council says the text removes the scanning obligation. The Internet Society’s coalition on encryption noted that both the Parliament and the Council stood against mandating client-side scanning in encrypted environments.
The mandate also contained a review clause. Three years after the regulation takes effect, the Commission must assess whether to make detection obligations mandatory, according to the Internet Society’s reading. That clause is why critics describe the compromise as a pause and not an end. A voluntary regime that can later be made mandatory is, in their view, the same system on a delay.
Four rounds, then six, and no deal
Talks between the Parliament, the Council and the Commission began on 9 December 2025. According to the Reclaim tracker, four rounds between December and May produced no agreement.
In mid-June, the tracker says, the Council’s legal service told governments that scanning private communications without suspicion remains unlawful under the current text. I could not find that advice published, so it rests on the tracker alone. A fifth round on 29 June failed over permanent scanning without suspicion.
The German technology outlet heise reported after one round that the Parliament’s negotiators saw substantial compromises on almost all points. It said they could not agree again on the core question, mandatory and suspicion-independent scanning of private communication, including on encrypted messengers. Progress was reported on other issues such as age verification. The Cypriot presidency, which ran for the first half of 2026, left the core question open.
The sixth round, on 29 September, agreed the tasks of the EU Centre and left detection in private messages open, according to the Reclaim tracker, which also reports a deal in principle on public content.
Its most recent update, dated 20 October, said that Council officials had met on a possible detection package, that compromise texts were due on 3 November and that political talks were planned for 8 December. The Council has not published those dates, and I found no published compromise text.
A reader should hold two things at once. The talks have narrowed the gap in several areas, and the Parliament’s negotiators describe real compromise. The central question, whether the law can order scanning of private and encrypted communication, has not moved in nearly a year. A deal in December would be a surprise, and a deal in the first half of 2027 depends on the next presidency’s priorities.
The vote Parliament won, then lost
Read also: Europe’s Digital ID Will Outlive Its Promises
The temporary exception is where the process looks least like ordinary lawmaking. Parliament first adopted a position on 11 March backing a shorter, narrower extension with added safeguards.
When the final deal with the Council collapsed, Parliament voted on 25 March 2026 not to extend, by 311 votes to 228 according to its own press release, and the exception lapsed after 3 April. For about three months, platforms had no legal cover for voluntary scanning.
EDRi describes what followed as a campaign to reverse the result. The conservative European People’s Party tried to reopen the Parliament’s position, and four Commissioners intervened by letter the night before a re-vote, according to the group.
EDRi notes that none of that broke a rule, and adds that it risked the Parliament’s credibility. Both of EDRi’s accounts come from an organisation that opposes the scanning law, and the Commission has not, in the sources I could open, given its own version.
The Council then revived the exception through an expedited procedure. It adopted a position on 2 July. On 9 July, Parliament voted at second reading on the Council’s text. Under that procedure a rejection needed an absolute majority of all members, which is a higher bar than a simple majority of those voting.
According to reports, 314 members voted to reject the Council’s text and 276 voted against rejecting it. Rejection at second reading needs an absolute majority of all members, 361 votes, so it fell short. Parliament did adopt amendments that, according to eucrim, exclude communication protected by end-to-end encryption and do not authorise client-side scanning, and the Council approved the amended text.
The Council gave final approval on 23 July, and the temporary regime now runs until 3 April 2028, according to Euronews and a legal commentary from the Maastricht-based ECA. Eucrim reports that the text was published on 28 July and entered into force on 31 July. EDRi described it as a mixed result.
EDRi reports that amendments aligning the text with Parliament’s position on the permanent law received more votes for than against, which it reads as a signal that there is no majority for mass surveillance. Other reports give higher vote totals, so the roll-call record should be checked. Opponents call the process undemocratic.
Whatever the label, the sequence matters for the permanent law. The Parliament’s refusal in March did not hold, since the exception was restored by July. It also shows how little pressure the lapse put on the Council.
What is still open
Four questions will decide how this ends. The first is whether the permanent law can contain any detection order that reaches private messages, and if so under what court supervision. The Parliament has said no to suspicionless scanning and to encrypted services, and the Council’s legal service has reportedly warned that the present text is still unlawful in this respect.
The second is age verification. Critics including the Electronic Frontier Foundation and Mullvad warn that provisions on risk mitigation could push services toward checking users’ ages or identities, which would end anonymous use of messaging services. Supporters say age assurance is a legitimate tool for protecting children, and the Parliament’s negotiators reported progress on it.
Our reporting on the EU Kids Act and on the planned ban on manipulation tricks follows the same tension in other laws.
The third is the review clause. If the compromise includes a duty for the Commission to reassess mandatory detection after a few years, the debate does not end with this law, it moves to the review. The fourth is time. The temporary regime runs to April 2028, which means there is no hard deadline forcing a deal this year, and presidencies change every six months.
One more issue sits outside the text. Surveillance tools bought for one purpose have a habit of spreading to others, and Europe’s record with spyware shows the same patterns of weak oversight. Our report on the Pegasus case involving an MEP who investigated Pegasus shows what happens when a surveillance capability exists and the checks on it are thin.
Who sits where
The map is not left against right. The Parliament’s majority has backed targeted measures with court authorisation and has refused scanning of encrypted services. The conservative group has been the main force pushing to restore the temporary exception, and some members from other groups voted with it. The vote splits have not followed a simple party line, and I did not find a published breakdown by group for these votes.
The Commission under Mr Brunner backs the law and, according to reports, prefers Parliament’s text to the Council’s compromise while holding to its original proposal. Governments are divided and have shifted.
Germany first opposed mandatory scanning, and Denmark, which held the presidency in the second half of 2025, moved from a text with detection orders to one without. Which governments would accept a new mandatory element is the question that the next presidency inherits.
Outside the institutions, the lines are clearer. Child protection groups such as the Internet Watch Foundation, ECPAT and the Canadian Centre for Child Protection back the law, and the Internet Watch Foundation itself admits in the press that end-to-end encryption is essential for privacy.
Digital rights groups, encrypted service providers, data protection authorities and academics oppose the scanning provisions. EDRi names Microsoft and Meta as examples of companies that scanned under the 2021 exception.
It is fair to ask who is affected by each outcome. Platforms and police agencies gain legal certainty from a stable framework. Encrypted service providers and users who rely on private channels lose if scanning extends to their messages. None of that settles who is right, but it explains why the fight has been so long, and why neither side trusts the other’s numbers.
What a citizen can check and do
You do not need to wait for a final text to follow this. The European Parliament’s legislative observatory lists the file under procedure number 2022/0155(COD), and it shows every official step and vote. The Council publishes some documents in its public register, though much of the bargaining text arrives late or not at all. Our guide to requesting public documents in Europe explains how to ask for the rest.
Roll-call votes in the Parliament are public, and they tell you how your own members voted on the temporary exception and on the Parliament’s position. That is the most direct check you have. Parliament’s website shows the votes by name, and the groups that track the file, such as EDRi and the Internet Watch Foundation, publish their own summaries, which you can compare. Read both, since each has an interest.
You can also ask the companies. Users can ask a provider whether it scans messages and which technology it uses. A provider that does not answer tells you something too. Under data protection law, you can also make a data access request to a company that holds data about you.
The safest assumption is that this is not finished. The temporary regime runs to April 2028, and the permanent law could still arrive with a scanning provision, with a review clause, or not at all. If you hold a view, your members of the European Parliament and your government’s representative in the Council are the people who will cast the votes, and both publish contact details.
The last point is about method. In this debate, nearly every number comes from someone with a stake, whether a children’s charity, a police agency, a privacy group or a company. That does not make the numbers false. It means each one is worth checking against a second source before you repeat it, which is the standard this guide tries to meet.
BASIS OF ANALYSIS
Basis of analysis: reporting by Euronews, heise and TechRadar, trackers and statements by EDRi, the Center for Democracy and Technology, the Internet Society, the Internet Watch Foundation and Reclaim The Net, and open letters by researchers, read in November 2026. Several advocacy sources are named as such in the text. Council negotiating documents were not available, so dates for the autumn 2026 talks are secondhand and could change.
Sources
- Reclaim The Net: EU CSA Regulation (Chat Control 2.0) tracker, updated 20 October 2026
- heise: Partial victory with a catch, EU Parliament temporarily defies chat control
- EDRi: Did the EU Parliament really vote not to protect children online? (11 May 2026)
- EDRi: The Chat Control 1.0 saga (4 August 2026)
- Center for Democracy and Technology Europe: response to the Parliament’s rejection of the Chat Control 1.0 extension
- ECA Maastricht: Two rights, one impossible law, Chat Control and child protection in the EU
- Euronews: Pourquoi Chat Control est au coeur du bras de fer numerique de l’UE (30 July 2026)
- Internet Watch Foundation: Why the EU’s temporary law must be extended (9 March 2026)
- EU Perspectives: Breyer warns Chat Control decision moves into 2026
- Internet Society: statement on the Council position on the CSA Regulation (12 December 2025)
- Help Net Security: Nearly 500 researchers urge EU to rethink CSAM scanning proposal (September 2025)
- Patrick Breyer: opinion by former CJEU judge Christopher Vajda on Chat Control
- TechRadar: Chat Control, EU Commissioner backs Parliament line on targeted monitoring