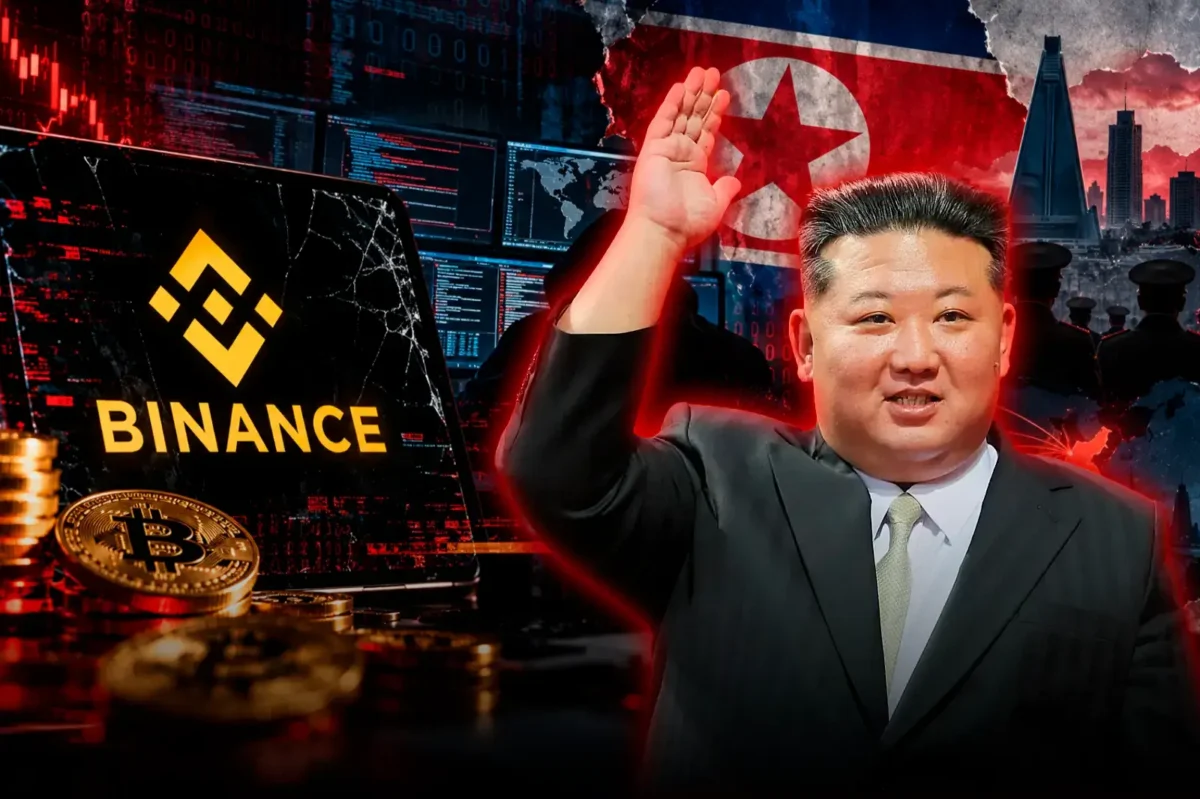
On Thursday 29 October 2026, shortly after 20:20 UTC, money began leaving Binance. Most of it was gone about twenty minutes later.
Table of contents
Blockchain analytics firm TRM Labs puts the theft at roughly $6.36 billion across ten blockchains. It is the largest crypto theft on record, ahead of the Bybit heist in February 2025, when $1.5 billion disappeared.
On Saturday the FBI named North Korea. The sums are so large that they hide the part that matters. The attackers got in through people, tools and approval routines, and no cryptographic lock was broken.
Twenty minutes, ten blockchains
Security firm Blockaid traced the Ethereum side. The target was a hot wallet (an online wallet an exchange uses for daily withdrawals) known as Binance 14. At 20:20 UTC, one transaction carried 50 authorisations. Then 167,464 ETH and 63 different tokens moved out.
The $6.3 billion figure is Binance’s own estimate. Outside tallies come in lower, and nobody has explained the gap. TRM’s $6.36 billion is the closest to Binance’s number, but it counts across ten chains, which makes comparison hard.
Binance suspended withdrawals at first while deposits kept working. It set aside $6.34 billion from its own funds and reserves and promised to cover every loss. It also says that, with partners, it has frozen about $3 billion.
Changpeng Zhao founded Binance in 2017. He pleaded guilty in 2023 to a felony over money laundering failures and stepped down as chief executive. President Trump pardoned him in 2025. After the hack he posted on X that “user funds are safe” and that it looks like a hack on Binance.
The signature nobody should have given
This part is technical, and worth taking slowly.
EIP-7702 is a feature in Ethereum’s Pectra upgrade from 2025. It lets an ordinary account hand control to a smart contract (a small program living on the blockchain). That is convenient for normal users, because several actions can be bundled in one transaction. It is just as convenient for a thief.
A delegation like that needs a valid signature from the account’s key. The attacker did not know the wallet’s current nonce (a counter that has to match exactly). So he sent 50 authorisations with consecutive numbers. Binance was still processing withdrawals from that wallet, and one of them landed.
Then the delegation did its job. The wallet’s behaviour was replaced by the attacker’s contract. The delegation does not remove itself, and unless it is revoked, the attacker can also reach funds that arrive later.
EIP-7702 itself was not the flaw. Several analysts stress that the feature worked as designed. The real question is who or what produced the signature.
Kok Tin Gan, cofounder and chief executive of cybersecurity firm NyxLab, put it bluntly. It looks like a single signature that gave the attacker a never-expiring, full-access token to a Binance hot wallet. He asked why stronger approval controls were not in place.
Binance said early on that it had found no evidence of a leaked private key. TRM places the problem in Binance’s signing infrastructure, not in the blockchain. A key can be untouched while the system around it produces a signature that no one should have approved.
From a job interview to a hot wallet
Binance’s first explanation pointed to a compromised laptop. The company has said it belonged to a DevOps engineer and gave access to a service container, from which unauthorised withdrawals were submitted. Chief executive Richard Teng later said there were additional points of breach and that the attack was more complex than one engineer’s access.
Read also: Suspected Binance hack halts withdrawals, no EU licence
Binance’s own report of 3 November describes how the attackers got there. Employees were approached by fake recruiters and invited to job interviews. During those interviews they installed tools that looked like ordinary developer software.
One was a tampered installer for Homebrew. Another was a malicious build of pyenv, where the file had grown from 3,344 to 3,414 bytes. Seventy bytes. That is all it takes.
The method is familiar. North Korean groups have spent years contacting developers with fake job offers and asking them to run code as part of a “test”. Binance’s head of security has said in the past that the exchange receives applications every day that it suspects come from North Korean operators.
Sources disagree on which platform the recruiting ran through. Some name LinkedIn, others an unnamed platform. We cannot settle that.
Four private firms and one agency
TRM Labs published its assessment on Thursday. It attributes the theft to TraderTraitor, which it describes as North Korea’s elite hacking unit, and says it makes the call with high confidence. Several features match earlier North Korean heists, including Bybit.
Chainalysis chief executive Jonathan Levin wrote on X that the hack was likely carried out by TraderTraitor. Elliptic has found that the stolen funds were mixed with proceeds from an earlier attack on the exchange Bitget, and that the laundering pattern resembles earlier North Korean operations.
On Saturday came the official confirmation. The FBI, together with the Secret Service and the IRS criminal investigation unit, issued an alert naming TraderTraitor and saying the hackers are mainly converting the stolen assets into Ethereum. The three agencies urged exchanges, analytics firms and other service providers to block transactions involving the wallets the hackers use for laundering.
That is stronger than a private opinion. It is still an assessment, and readers should know what it rests on: pattern recognition. Same methods, same laundering venues, same infrastructure as in the Bybit case, where the FBI also pointed to TraderTraitor.
Two caveats apply. The attributions lean on each other, and it is not clear how much of the FBI’s conclusion rests on the private firms’ work. The firms also have a commercial interest in showing that they can follow the money. That does not make the conclusion wrong. It makes it a probability judgement from parties with something to gain.
Binance has not itself confirmed North Korea. A spokesperson said only that the company is working closely with law enforcement to identify the criminals.
We found no evidence in anything we could read for theories of an inside job or Russian hands.
The background is well documented. North Korea has made crypto theft a revenue stream under heavy UN sanctions. South Korea’s intelligence service estimated in 2022 that North Korean hackers had stolen 1.5 trillion won, about $1.1 billion, over five years. One evening has now exceeded that by a factor of six.
Three billion frozen, the rest unknown
Freezing only works where someone can press the button. That means stablecoins (cryptocurrencies pegged to the dollar), where the issuer can block a wallet. Tether, Circle, Ripple and World Liberty Financial have frozen amounts, and the Arbitrum Security Council has done the same on its network. Circle chief executive Jeremy Allaire says more than 800 million USDC is frozen in cooperation with authorities, and Tether chief executive Paolo Ardoino says just under 1.57 billion USDT is frozen.
Native assets such as bitcoin, ether, XRP and solana have no issuer. Nobody can freeze them. The FBI says the hackers are converting mainly to Ethereum, and that is no coincidence.
Binance puts frozen assets at about $3 billion, but the split by source and chain has not been published. Reported freezes vary from tally to tally, and we found no independent count. “Three billion” is Binance’s number, not a verified one.
Frozen is not recovered. Frozen funds sit still. Getting them back is decided by lawyers, issuers and courts, and it takes a long time.
The laundering playbook
The laundering follows a pattern analysts know from earlier cases. After the 2025 Bybit heist, Elliptic described how Lazarus typically first swaps stolen tokens into a native asset such as ether and then runs them through mixers like Tornado Cash and across bridges between blockchains.
Researchers have already seen that an address funded through Tornado Cash submitted the first authorisations against Binance’s wallet. Later movements have been observed through THORChain, bridges and loans on Aave, where the stolen assets can serve as collateral.
The FBI expects more of the same. Its alert says the hackers will push further assets through decentralised finance platforms and exchanges that allow rapid swaps between assets. Every service that chooses not to block is a link in the chain.
After Bybit, the anonymous exchange eXch denied laundering money for Lazarus, even though Elliptic and others said it had processed tens of millions of dollars. The same question will come back.
Bigger every time
Bybit lost $1.5 billion in February 2025. The FBI pointed to TraderTraitor then too. Before that, the records were Poly Network with $611 million in 2021 and an attack on Binance itself in 2022 for $570 million.
Each record was set by an attack on a central service where a few people and a few keys hold enormous sums. That is a convenient target for a state-run hacking group with time and patience. And it can strike again, because the same weaknesses exist elsewhere: developers with administrator rights, permissions that never expire, and approval chains that can be talked into signing.
Kok Tin Gan’s point about missing controls is therefore more than a footnote. It shows where regulation can make a difference: the internal controls before a signature leaves the building. The blockchain held.
In the United States, the commodities regulator CFTC has meanwhile argued that crypto exchanges should register. That does not answer this hack, and it still shows where the debate is heading.
Binance left Europe before the bill came
European customers were not directly hit. Binance is leaving the EU because it did not obtain the licence required under MiCA, the EU regulation on crypto-assets. An attempt to get licensed through Greece failed. The wind-down in the EU began on 1 July 2026.
MiCA is enforced by national supervisors, and a licensed provider can be checked against a public register. That is the practical test for a European user: can the platform show the paperwork? A provider that cannot is outside the regime, whatever its size.
The case tells us something about the balance of power. The world’s largest exchange had no European licence and could still promise to cover a loss of more than six billion dollars from its own funds and reserves. The size of that pocket is an argument for supervision. It is also an argument that supervisors must be able to see what is in it.
We found no figures on how many European users held funds on Binance before the exit, and no statement on the case from EU supervisors. Both are gaps that the European Commission, national authorities and the EU’s cyber agency could fill.
What we cannot confirm
We have not read the FBI alert in its original form, because the page could not be retrieved. We saw its contents through a secondary report. Binance’s report of 3 November we have seen only in secondary summaries, and we found no result of an independent proof-of-reserves check.
Several central numbers therefore stand as Binance’s or an analyst’s, not as verified facts: the $6.3 billion, the $3 billion frozen, and the refilled amount, which in different accounts lies between 90 and 98 percent.
And the question itself remains. Who approved a signature that handed a stranger the key to a hot wallet? Binance has so far answered with a report. The criminal investigation, in which the FBI and the Secret Service take part, is not finished.
BASIS OF ANALYSIS
Basis of analysis. This analysis rests on the FBI alert as reported, an AP review of the analytics firms’ attribution, Blockaid’s technical trace of the transaction and Binance’s own statements about the sequence of events. Only the FBI alert and the private firms’ assessments are primary sources for the attribution. Binance’s 3 November report, the result of any proof-of-reserves check and the number of affected European users could not be confirmed.
Sources
Korea Times: FBI says N. Korea responsible for over $6 bil. crypto theft from Binance
The FBI’s attribution to TraderTraitor, the conversion to Ethereum and the call to block addresses.
Associated Press: Blockchain intelligence firms link North Korea to $6.3B hack on Binance
TRM’s and Chainalysis’ attribution, Kok Tin Gan’s assessment, Binance’s statements and Zhao’s background.
Block Media: Binance 63억달러 해킹, 이더리움 EIP-7702 악용
Blockaid’s account of the 50 authorisations, the nonce mechanics and the amounts from Binance 14.
Börse-Global: Ethereum: Angriff über EIP-7702
Binance’s first explanation (DevOps laptop), Richard Teng’s statement, the $6.34 billion set aside and the $3 billion frozen.
MEXC News: What Role Did EIP-7702 Authorizations Play in the Binance Hack?
The distinction between key theft and a compromised signing infrastructure, and the Tornado Cash funding.
Elliptic: Bybit hack – largest in history
Lazarus’ typical laundering pattern, used as the benchmark.
Decrypt: Bybit Funds on the Move, Could be Headed for Bitcoin Mixers ‘Next’: Elliptic
How the laundering unfolded after the Bybit heist, and eXch’s denial.
arXiv: EIP-7702 Phishing Attack (Qi et al., December 2025)
How EIP-7702 delegation works and its use in crime.