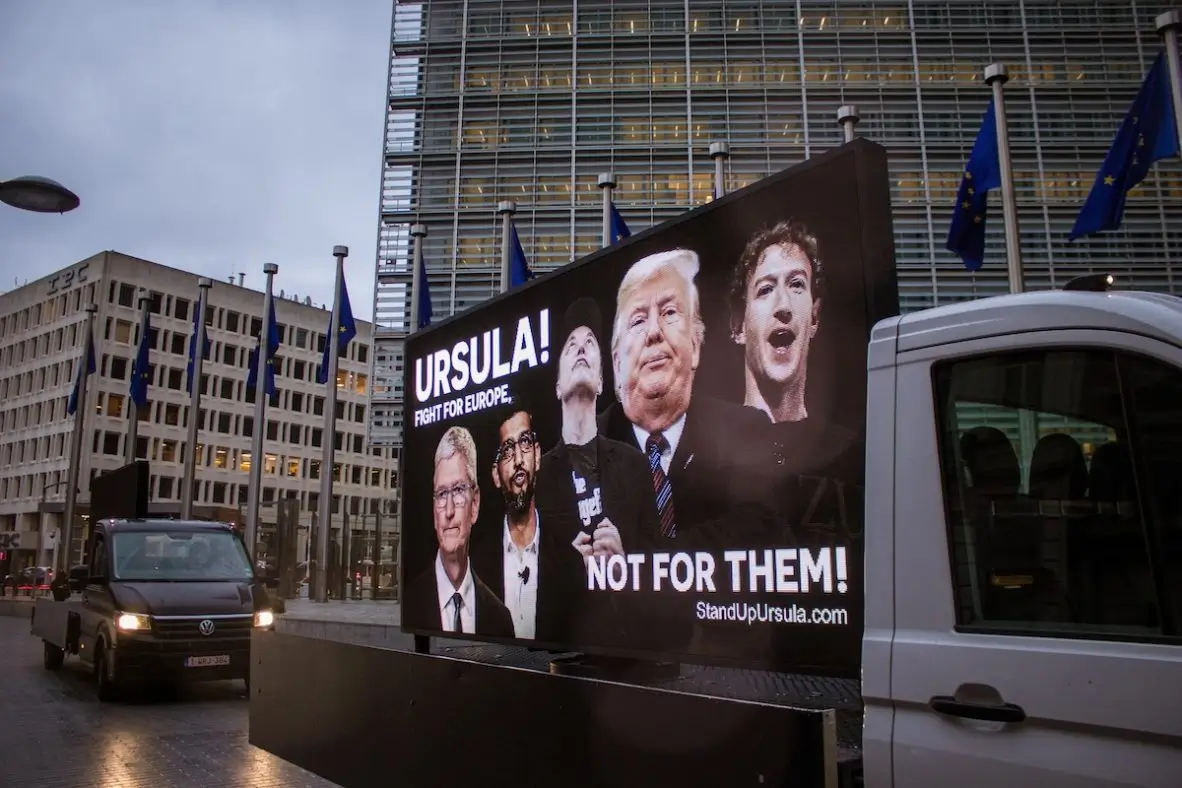
Europe’s data protection rules decide what companies may do with information about you, from the cookie banner on a news site to the training of AI models. In November 2025 the European Commission proposed changes to those rules in a package called the Digital Omnibus. Two Brussels watchdog groups say the proposals follow Big Tech’s wish list closely. The Commission strongly disputes that.
Table of contents
Almost a year on, the record is mixed. The Council kept the core definition of personal data intact in October 2026. The AI half of the package was formally approved this summer with the delay that industry groups had asked for. The data half is unfinished, and Parliament has not yet set its position.
Eight changes against a pile of lobbying papers
Corporate Europe Observatory and LobbyControl published their analysis in January 2026. Their method was direct: they set the Commission’s proposals beside the position papers of Big Tech companies and their trade associations and looked for matches. They compared eight changes to the GDPR and the AI Act and report close matches for most of them.
The examples are specific. Under the proposal, pseudonymised data would stop counting as personal data for an entity that cannot identify the person. The groups tie that change to papers from DigitalEurope and Microsoft Germany.
Treating AI training on personal data as a legitimate interest is tied to CCIA, DigitalEurope and Dot Europe. Moving parts of the cookie consent rules into the GDPR, with broader exceptions, is tied to Google and Microsoft. Allowing people’s access requests to be refused for abuse is tied to a Google paper from August 2025.
On the AI Act, the groups link the removal of mandatory public registration for high-risk systems to DigitalEurope and Dot Europe. A delay of almost 18 months for high-risk rules is tied to CCIA, DigitalEurope and Meta. One change gets different treatment: easing the GDPR’s limits on automated decisions, which the groups attribute mainly to insurance lobbying.
The pseudonymisation change carries weight because of the test behind it. The Commission’s text used a test based on the controller’s own means of identification, so the same dataset could count as personal for one company and fall outside the GDPR for another.
The groups describe their work as critical analysis, and the lobbying links are their own characterisations. A match between a paper and a proposal means the two say similar things. Authorship is a separate question that the analysis cannot settle.
Meetings and budgets behind the matches
The same analysis puts numbers on access. Industry lobby spending rose from €113 million in 2023 to €151 million, an increase of 33.6%. Meta met MEPs from the ECR, Patriots and Europe of Sovereign Nations groups 38 times in the current mandate. In the previous mandate it met a far-right MEP once.
The week of 8 December 2025 shows the pattern. Meta met four far-right MEPs, and most of those meetings mentioned the Digital Omnibus. Days after the package launched, the head of public affairs at Google France joined a Strasbourg dinner hosted by six Rassemblement National MEPs.
Read also: Brussels Fined Big Tech 2.46 Billion. Washington Threatens Tariffs
Meetings with legislators are routine in Brussels, and the sources reviewed carry no reply from either company. The groups read the pattern as a priority: lobbying of far-right groups became a particular focus for Meta, and to a lesser extent Google. Parliament must adopt a position before talks on the data half of the package can begin, so the voting arithmetic there carries weight.
The Commission’s answer
The Commission strongly disputed the report. A spokesperson said the package was developed through “a transparent and comprehensive process” that drew on civil society, small businesses and academia. The Commission describes the GDPR changes as a “face-lift” and frames the whole agenda as making the EU more competitive.
That position has a logic. Industry and the Commission can reach similar conclusions about compliance costs without one writing the other’s text, and the Commission’s stated aim is a digital single market that serves companies of every size. A reader who favours simplification sees the overlap as a shared diagnosis.
That reading can be checked against what independent regulators and the Council made of the substance. Their record is split.
What the regulators accepted and refused
A joint opinion of the European Data Protection Board and the European Data Protection Supervisor, issued in February 2026, sorts the package point by point. The two bodies strongly oppose the new definition of personal data. They say it goes beyond a targeted fix, conflicts with Court of Justice case law and would significantly narrow the concept.
They also reject giving the Commission power to decide, through implementing acts, when pseudonymised data stops being personal. That is the first change on the groups’ list, and it is the one regulators resisted hardest.
On other points the regulators partly agree with the Commission. They accept that legitimate interest can sometimes serve as a basis for developing AI, while noting that the GDPR already allows it. They back a narrow derogation for incidental sensitive data in AI training, a higher threshold for breach reports, a 96-hour deadline in place of 72, and a single EEA-wide entry point for notifications.
On cookies they welcome less consent fatigue and machine-readable choice signals, and want exemptions kept strictly limited. On access requests they support clarifying misuse, and say abuse should turn on clear signs of bad faith, not the requester’s motives. The opinion has no binding force, and the institutions are expected to weigh it in the talks.
The Council keeps the definition
On 21 October 2026 the member states’ ambassadors approved the Council’s negotiating mandate. It keeps the GDPR’s existing definition of personal data and rejects the Commission’s change to Article 4(1). A new Article 25a on pseudonymised data takes the place of that change. Such data is not personal for a third party that cannot identify the person, and it stays personal for processors acting for a controller.
A new recital 27c gives the European Data Protection Board the job of issuing an opinion on pseudonymisation and anonymisation after public consultation, a task that Commission implementing acts would otherwise have covered. That moves the call from the Commission to the regulators’ own body.
On AI, legitimate interest stays available as a legal basis, and a new recital says developing AI is not in itself a legitimate interest. The Commission’s unconditional right to object gives way to the general right under Article 21, so controllers can continue if they show compelling grounds. The exception for sensitive data is limited to residual data that appears incidentally.
Read also: Brussels Pushed Its Hardest AI Rules Back 16 Months
On cookies, the rules stay in the ePrivacy Directive. New consent exemptions cover media audience measurement and contextual advertising measurement, both with pseudonymisation. After a user rejects cookies, consent cannot be requested again for four months, against six in the Commission’s text.
The Council also deleted the Commission’s duties on honouring automated browser privacy signals. That is a protection the regulators had welcomed, and its removal is the clearest place where the mandate moves toward industry.
The breach rules keep the 96-hour deadline and the high-risk threshold. The mandate rejects a single EU-level entry point for incident reports and proposes national ones, which departs from the regulators’ backing for a single EEA-wide point. The Board, not the Commission, would approve the lists of high-risk breaches.
The AI delay is approved
The AI part moved faster. Parliament and the Council have both formally approved the Digital Omnibus for AI. The new deadline for standalone high-risk AI systems is 2 December 2027, and for high-risk systems embedded in products it is 2 August 2028. The original date was 2 August 2026. The changes take effect after publication in the Official Journal.
The shape of the package matters here. The Commission put the AI changes and the data changes in separate instruments, and they have moved at different speeds. The AI instrument has been formally approved, while the data instrument is waiting for Parliament.
The delay is the item on the groups’ list with the clearest lobbying trail, since, in the groups’ account, CCIA, DigitalEurope and Meta all asked for it. Supporters answer that companies need more time to comply, which is how the co-legislators framed the decision.
The sources reviewed do not show whether the removal of mandatory public registration survived in the final text. The point carries weight, because public registration is what lets outsiders see which high-risk systems are in use.
What is still open
The data half of the package has not reached the negotiating table. Parliament must adopt its position first, and then talks with the Council and the Commission can start. The final text needs approval by both institutions.
Legal commentators expect the main disputes to be personal data and pseudonymisation, legitimate interest for AI, the cookie rules and the model for incident reporting. On each of those, the lobbying papers and the regulators’ opinion pull in different directions.
Member states signalled opposition to the definition change as early as February, and the October mandate confirms it. The regulators’ February opinion and the member states’ October mandate land in the same place on the definition.
The definition of personal data is intact in the Council’s mandate. Whether it stays that way will be settled in talks that cannot start until Parliament picks a side.
Part of our guide to Europe’s digital dependence: Europe Runs on Computers It Does Not Own
Part of our guide to who writes Europe’s laws: Who Writes Europe’s Laws and Who Watches Them
BASIS OF ANALYSIS
Basis of analysis. The analysis rests on six sources. The lobbying comparison comes from two advocacy organisations and is presented as their characterisation. The regulators’ opinion and the Council mandate are described through law-firm and trade-press summaries. The Commission’s proposal text, the Council mandate document, Parliament’s drafts and any company replies were not examined directly.
Sources
- Corporate Europe Observatory and LobbyControl: Article by article, how Big Tech shaped the EU’s roll-back of digital rights (January 2026) – the eight-change comparison, meeting counts and spending figures.
- Euractiv via Freevacy: Civil society report warns Digital Omnibus package parrots big tech talking points (14 January 2026) – the Commission’s response.
- Covington Inside Privacy: EU regulators issue opinion on revisions of GDPR and other data laws (February 2026) – the EDPB and EDPS joint opinion, point by point.
- Cuatrecasas: Digital Omnibus, EU Council establishes position (27 October 2026) – the Council mandate of 21 October 2026 in detail.
- IAPP: EU member states finalize Digital Omnibus negotiating stance (October 2026) – the Council stance on personal data, cookies and incident reporting.
- Danish Standards: Digital Omnibus for AI approved (10 July 2026) – formal approval and the new high-risk deadlines.