On 12 November a capacity problem at one American company stopped email, video meetings and shared files for banks, courts, schools and governments in what Downdetector counts as 74 countries and territories. Europe’s cloud dependence is usually filed under procurement. For the offices locked out that day, the question was whether work could continue at all.
Table of contents
- One outage reached seventy-four countries
- Three companies own the cloud under European life
- Where cloud dependence meets American law
- A sovereign cloud with a parent in Seattle
- When the network can be capped from outside
- Palantir and the contracts few citizens can read
- Who has left Palantir, and who cannot
- Rules written for systems Europe rents
- Brussels answers with a law of four levels
- What the four levels leave open
- The best case for staying
- The bill for a European alternative
- Five questions before the next contract
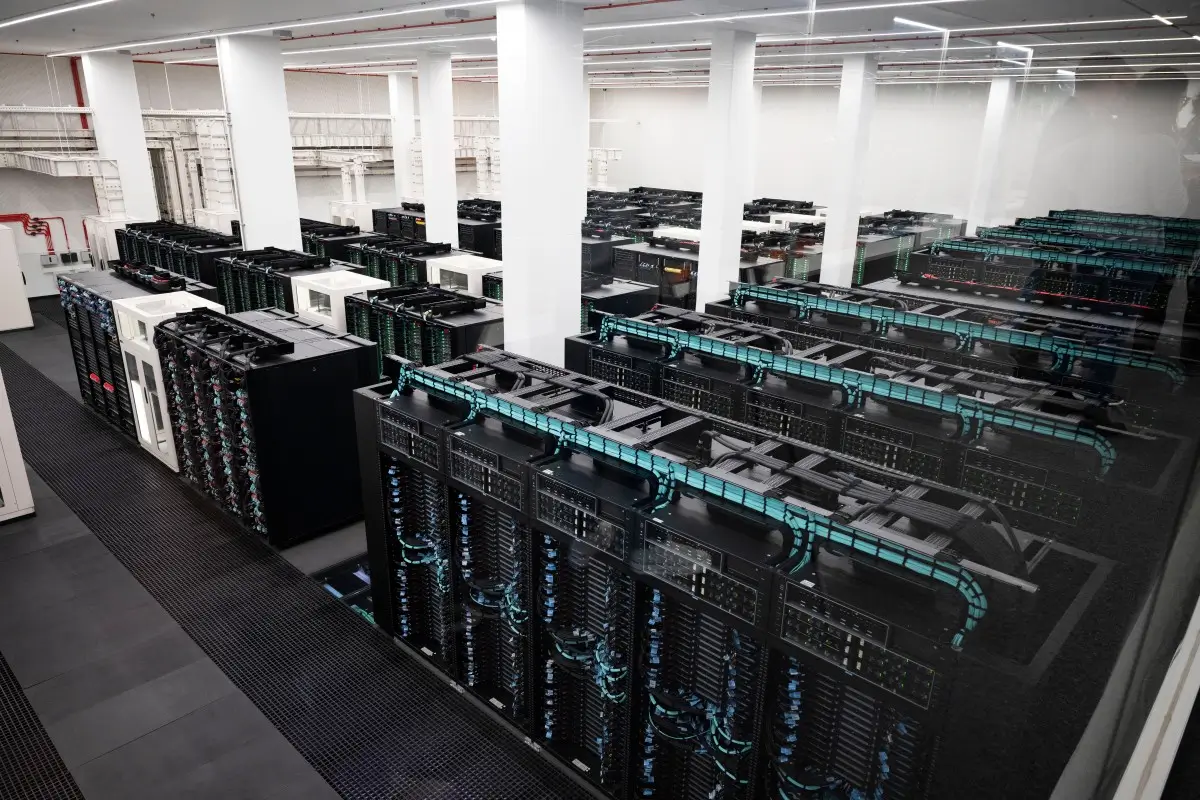
Three US companies, Amazon, Microsoft and Google, hold about 70 percent of the European cloud market. European providers hold about 15 percent. The same infrastructure carries the systems of police forces, hospitals and armies, and an American law lets US authorities order a US provider to hand over data wherever it is stored.
This guide follows that dependence from an outage to the law. It looks at who owns the machines and which legal system reaches them, then at a satellite network and a data contractor that governments cannot easily replace. It ends with the Commission’s new proposal and the questions a public buyer can put to any supplier.
One outage reached seventy-four countries
The Microsoft outage began around noon on the US East Coast on Thursday and was still widespread on Friday morning, when Europe woke up. Outlook, Teams and shared files were down for companies, banks, courts and governments. Microsoft says a cybersecurity breach did not cause it.
In Australia, courts and schools were among those hit. New Zealand’s foreign ministry said its ability to receive email was affected, embassies and consulates included. Downdetector logged well over 100,000 reports for Outlook alone at the peak, a figure that understates the problem because most affected users never file one.
Microsoft’s own accounts of the cause differ. One service notice said servers had become unexpectedly unavailable and that a rise in traffic was not behind it. A later notice pointed to traffic management imbalances. The company gave no date for full restoration while the outage ran. Our report on the outage sets out the record and how customers can claim credits.
This was not the first time. When Azure failed on 29 October 2025, the Dutch rail operator NS lost its travel planner and ticket machines. Of the November outage, Tommaso Valletti, professor of economics at Imperial College Business School and the Commission’s chief competition economist from 2016 to 2019, said it showed “the downside of depending so heavily on a handful of large US tech companies”.
Dutch Green MEP Reinier van Lanschot put the risk plainly: “Our critical systems run on someone else’s technology, and someone else can switch it off.”
Three companies own the cloud under European life
Synergy Research Group, which tracks the market, puts European cloud revenue at 61 billion euros in 2024, six times its size in 2017. European providers more than tripled their own revenue over those years, and their share still fell from 29 percent in 2017 to 15 percent in 2022. The share has stayed near 15 percent since.
Amazon, Microsoft and Google hold about 70 percent between them. The largest European providers, SAP and Deutsche Telekom, hold about 2 percent each. Synergy’s chief analyst, John Dinsdale, expects European providers to struggle to win back lost ground.
The Commission puts the same dependence in euros. It says the EU spends 264 billion euros a year, mostly on proprietary IT products and services from US suppliers, and that US cloud companies control more than 70 percent of the EU cloud market. It also says sovereignty goes beyond data transfers and relates to operational autonomy.
Where cloud dependence meets American law
The CLOUD Act, which the US Congress passed in 2018, lets US authorities order a provider under US jurisdiction to hand over data it controls, whether the data sits in the United States or abroad. A data centre in Frankfurt or Dublin owned by a US company is covered. A provider with no American parent and no significant US operations is not.
The law sets out a process for such orders and gives US agents no automatic access. For European customers the difficulty is the collision with their own law. The European Data Protection Board and the European Data Protection Supervisor concluded in July 2019 that, without an international agreement, the lawfulness of such a disclosure of personal data “cannot be ascertained”.
The only exception they named covers cases where disclosure protects the vital interests of the person whose data is involved. A provider holding European personal data can therefore face an order from Washington that European law does not support.
A sovereign cloud with a parent in Seattle
The industry has noticed the problem and sells an answer. Amazon Web Services launched its European Sovereign Cloud in Brandenburg in January, run by new companies set up for the purpose. AWS says they are incorporated in Germany and run exclusively by EU residents.
Critics point to the parent. AWS is part of Amazon, a Seattle company that stays subject to American law, and the open question is whether a German subsidiary can shield data from an order served on its parent. The Commission’s proposal tries to settle it in law, with levels that apply different tests for foreign control.
About two dozen European cloud chief executives, writing through their trade group CISPE in March, warned against what they call sovereignty-washing. Sovereignty, they wrote, must be “defined by control, not simply by having EU presence”.
When the network can be capped from outside
Ukraine’s interceptor drones, which hunt Russian jet-powered Shahed drones, lose their satellite link when they fly faster than about 160 km/h. The limit sits in Starshield, the military version of Starlink. The restriction was first recorded overnight on 13 to 14 October, and Ukrainian forces received no warning, according to Serhiy Beskrestnov, an adviser to President Zelensky on military technology.
Connectivity above 400 km/h was confirmed restored on 24 October. On 12 November Zelensky said the limit, 161 km/h, was back and that some strikes had got through. Nobody has taken responsibility, and reports on who acted differ. Elon Musk wrote that Starshield systems are “owned and controlled by the US government” and that any limits are decided by the US military and ultimately the president.
Pentagon chief Pete Hegseth said “We haven’t pulled anything back” and tied the limits to Starlink’s terms of service. Musk points to the US military and the president, Hegseth to a contract term, and both cannot be the operative rule.
Europe’s answer is a timetable. The EU’s own system for pooled government satellite capacity, GOVSATCOM, began operating in January on eight satellites from five member states, and Defence and Space Commissioner Andrius Kubilius called it “the first step”. The larger IRIS² constellation is now expected to enter service in 2029.
Read also: European Governments Went Dark Over a PHP Flaw Whose Fix Stalled
Kubilius has also said there is “no process for mobilising European assets for our joint defence”. Ukraine’s access agreement with Washington expires in mid-2027. Against a network it does not own, Europe has a service with eight satellites and a constellation due in 2029. Our report on Starshield follows the timetable.
Palantir and the contracts few citizens can read
A cross-border investigation led by the Dutch outlet Follow the Money, with partner newsrooms in 17 countries, counted at least 11 European countries with national-level contracts with Palantir, the US data analytics company. Palantir has offices in 14 European countries. The investigation puts the sums paid by the authorities it could count at about 1.4 billion euros and says the real figure is higher, because some governments, the Netherlands and Sweden among them, will not comment.
Defence ministries or armed forces are customers in eight of the 11 countries. National police forces in at least five countries, Finland, Norway, the Netherlands, Sweden and Denmark, use its Gotham platform, and German state police forces use it too. Norway’s police and customs paid about 52 million euros between them, and Germany’s contracts add up to between 47 million and 86 million euros.
In Britain, a Palantir-led consortium won the National Health Service data platform in November 2023, reported as a 330 million pound contract in some coverage and as worth up to 480 million pounds in others. About 198.4 million pounds had been paid by March 2026. One contract carries three figures, and each measures something different. Our report on Palantir in Europe maps the German state contracts and the answers that governments withhold.
Who has left Palantir, and who cannot
Some governments have started to leave. France’s domestic intelligence service will not renew its contract again, Norway’s national police are not renewing one that expires in 2027, although Norwegian customs had theirs extended to 2030, and Spain is declining to renew its only contract. Switzerland’s army and armaments office examined Palantir several times and declined.
The Netherlands has used Palantir since 2010. In June its defence state secretary, Derk Boswijk, told parliament that a full alternative should exist within two years. Germany’s cyber defence chief, Vice Admiral Thomas Daum, called it “simply inconceivable at the moment” to give industry staff access to the national database.
Francesca Bria, honorary professor at University College London’s Institute for Innovation and Public Purpose, says the reliance creates “a dependency that is almost impossible to undo”.
Palantir says sovereignty depends on “who controls the data, the decisions, and the mission”. It says it has worked with European governments since 2011 and that more than a fifth of its staff are in Europe.
The practical side of that argument is real. A hospital data platform or a police analysis system cannot be swapped over a weekend, and the Dutch two-year timetable shows that no ready replacement exists today. Two decision points come within six months: the NHS contract reaches a break clause in February 2027, and Bavaria’s current contract term ends in April 2027, and the state plans to extend it by at least a year.
Rules written for systems Europe rents
Europe has written the world’s most detailed AI rules, and the strictest of them have just slipped. Obligations for high-risk AI systems, used in hiring, credit scoring, border control and courts, were due on 2 August 2026. Parliament and Council approved a delay in June, it became law in July, and the obligations now apply from 2 December 2027, sixteen months later. Our report on the delay lists what moved and what did not.
Two Brussels watchdog groups say the Digital Omnibus, the Commission’s package of changes to data and AI rules, follows Big Tech’s wish list closely. The Commission strongly disputes that, and the Council kept the core definition of personal data intact in October. The record is mixed.
The fines show the same pressure from the other side. The Commission has fined platforms 2.46 billion euros under its two digital laws since 2025, and Washington has threatened tariffs. The dispute is far from over, because appeal is the default.
Here is the enforcement problem. A regulator with domestic alternatives can say no and mean it. One whose economy runs on foreign platforms has to ask what the supplier will say, and what its government will say next. Our opinion piece on this problem argues that Europe writes AI rules for systems it rents.
Brussels answers with a law of four levels
On 3 June the Commission proposed the Cloud and AI Development Act, known as CADA. It sets up one EU framework for judging how sovereign a cloud service is, ties the result to who may supply public bodies, and aims to at least triple EU data centre capacity within five to seven years.
The framework has four “Union assurance levels”. At level 1 a provider assesses itself and declares that it conforms. Levels 2 to 4 need an independent audit. Level 1 requires the provider to be established in the Union, with infrastructure and customer data staying in the Union unless the public body says otherwise.
A provider controlled from outside the Union must also show, with independent evidence, that no law or practice in the controlling country forces it to report unpatched software vulnerabilities to that country’s authorities before they are known to be exploited.
Level 2 adds measures that must prevent third-country access to customer data and stop the provider being forced to apply foreign sanctions or embargoes that are not legitimate under EU or national law.
At level 3 the provider and its subcontractors must be free of third-country control, with a narrow derogation if the Commission recognises a third country by a separate act. Level 4 allows no derogation, and the provider must keep effective control over its software components.
Public bodies must buy at level 1 as a minimum. Where a risk assessment finds an activity relevant to public order, they may use only services at levels 2 to 4, with limited exceptions if no suitable recognised service exists or compliance would cost disproportionately.
What the four levels leave open
Critics read the levels as a gate that lets US firms through at most of them. Filippo Gualtiero Blancato, author of a policy brief for Harvard’s Belfer Center, concludes that US hyperscalers would qualify at level 1 and could qualify at level 2 by partnering with EU companies that hold majority ownership.
At level 3, he writes, they would not qualify without a Commission exception, and he puts level 4 at about 1 percent of public sector data.
ARTICLE 19, the freedom of expression organisation, argues that the framework sets the terms on which the same few companies keep taking part, and that only level 4 excludes non-EU providers. It quotes the Commission’s aim to keep “most of our market open to like-minded partners”.
Enforcement is a second worry. A provider applies to the authority of the country where it is established, other member states then have 60 days to object, and a reasoned objection goes to the Commission for a binding decision. Blancato warns that hyperscalers could obtain contracts with more lenient states.
European providers want a harder line. The CISPE chief executives asked Commission Executive Vice-President Henna Virkkunen to reserve procurement shares for European cloud providers, or at least to follow a rule of buying European, ensuring resilience or explaining why not.
The proposal has no explicit Buy European mandate, which Blancato presents as a choice made to avoid US retaliation. Parliament’s draft report on the act calls on public authorities to buy more cloud services from European providers.
Read also: Europe needs a revolving door rule for AI
The fight is old. The EU’s cloud certification scheme, EUCS, has never been adopted. A third draft in March 2024 removed its sovereignty requirement and left the matter to national regulators, and the Commission’s own CADA text says the scheme has yet to be adopted and that work will resume. A French cybersecurity outlet reads the new four-level system as a close copy of the provisions removed in 2024.
The best case for staying
The strongest case for the present arrangement starts with customer behaviour. A Bitkom survey found that 85 percent of German companies say Germany is too dependent on US cloud providers, and 71 percent use one. IDC found that only 4 percent of European organisations plan to use local providers exclusively.
The Commission says the market stays open to partner countries whose providers meet the assurance levels. Ulrich Ahle, chief executive of the Gaia-X association, says sovereignty should rest on “trusted interdependence”, a model in which organisations keep control while taking part in open, federated ecosystems.
The argument has weight for the biggest systems. Replacing a cloud that runs a hospital network or a ministry’s email takes years, and the Dutch two-year timetable for Palantir shows how long an exit takes even when the will exists. A rule that bars suppliers before replacements exist would leave public bodies without a service.
The reply from the dependence side is that the exits the proposal creates are narrow. Level 4 covers about 1 percent of public sector data in Blancato’s estimate, and a provider can serve nearly everything else at level 1 or 2.
The bill for a European alternative
The Commission describes CADA as an instrument to boost private investment in cloud and data centres. That money has other claims on it. When Alphabet reported on 28 October that free cash flow was negative 9.1 billion dollars for the second quarter in a row, its shares fell by roughly 10 to 13 percent the next day. Amazon’s long-term debt of about 173 billion dollars has more than doubled since December.
Brussels set a target for buildings, and investors are setting one for cash flow. Our report on AI spending and the tripling target follows both.
Europeans already help finance the American buildout. Four ECB staff members counted that US big tech companies made up just under 10 percent of gross new issuance of euro-denominated corporate bonds up to 20 August, and they say pension funds and insurers in the euro area are among the buyers. The pattern is growing.
European builders exist. OVHcloud and Scaleway won places on the Commission’s sovereign cloud contract, worth up to 180 million euros, and Stackit, owned by the Schwarz Group, is building an 11 billion euro AI data centre in Brandenburg.
London-based Nscale is building a campus in West Virginia, where an agreement reported at about 44.6 billion dollars in August covers capacity, as our report on its plans describes.
Capacity needs power. Data centres use about 2.5 percent of EU electricity today, and the International Energy Agency projects more than 3 percent of EU demand by 2030. The planning fights are already running, from Amsterdam’s restrictions to the Zeewolde campus that farmers helped derail. Our report on the data centre plans follows the planning fights.
Five questions before the next contract
A public body does not have to wait for the final law to ask what the assurance levels would ask. Five questions cover most of it.
Who owns the supplier, and which courts can order it to hand over data? A European data centre with an American parent answers to both legal systems.
Who holds the keys and runs the support desk? Under the second level, support must be initiated and performed within the Union.
What happens on the first day of an outage, and is the fallback written down and tested? On 12 November, offices without a plan B found out. The outage report lists the questions to ask before the next procurement round.
Can the contract be exited within a year, and who pays for the move? The second level of the proposal asks for a documented migration plan in case the vendor fails or a third country imposes restrictions.
Who can switch it off? In October the people named as responsible for the Starshield cap gave versions that do not line up.
Europe wrote the rulebook for the digital age and left much of the hardware to others. The proposal would set conditions on that arrangement, and its minimum level is a provider’s own declaration. Until the higher levels carry real contracts, every outage, cap and renewal will answer the question of who is in charge, and the answer will keep coming from the supplier.
BASIS OF ANALYSIS
Basis of analysis. The article rests on 15 sources. Two are official documents: the Commission’s proposal and the data protection authorities’ 2019 assessment. Figures on the Microsoft outage, Starshield and Palantir come from earlier ExtraFokus reporting, whose sources are listed there. The proposal is a draft, so the criteria described here may change in negotiation.
Sources
- European Commission: Proposal for a Cloud and AI Development Act, COM(2026) 502 final (3 June 2026) – assurance levels, procurement rules and the capacity target.
- Synergy Research Group: European Cloud Providers’ Local Market Share Now Holds Steady at 15% (24 July 2025) – market size and provider shares.
- Tech Policy Press: EU unveils sweeping tech sovereignty push (3 June 2026) – Commission figures on spending and market share.
- EDPB and EDPS: Annex to the joint response on the US CLOUD Act (July 2019) – lawfulness of disclosure without an international agreement.
- CISPE: Put Cloud Sovereignty, Resilience, and Fair Competition at the Heart of CADA (17 March 2026) – the cloud providers’ five principles.
- Gaia-X: Gaia-X welcomes the EU Cloud and AI Development Act – the association’s position on interdependence.
- Belfer Center: EU Tech Sovereignty Package Policy Brief – a reading of the assurance levels and enforcement.
- ARTICLE 19: Sovereignty washing, a critical reading of the EU’s Tech Sovereignty Package – critique of the framework.
- Euronews: Can Europe’s tech firms really replace Amazon, Google and Microsoft? (14 November 2026) – survey figures, expert comments and Parliament’s position.
- The Nerve: investigation into Palantir contracts across Europe, led by Follow the Money – contract counts, values and exits.
- EU Institute for Security Studies: Technical is political, when a cloud certification scheme divides Europe – history of the EUCS sovereignty clause.
- ExtraFokus: The Microsoft outage showed who owns your uptime (13 November 2026) – the outage record and its sources.
- ExtraFokus: Starshield, Ukraine’s drone defence runs on a network Europe does not own (12 November 2026) – the cap and Europe’s timetable.
- ExtraFokus: Karp’s Swedish forest, Europe’s Palantir problem (12 November 2026) – contracts, exits and decision points.
- ExtraFokus: Investors flinch at AI spending, Brussels targets triple (30 October 2026) – investor reaction and the tripling target.